Activity
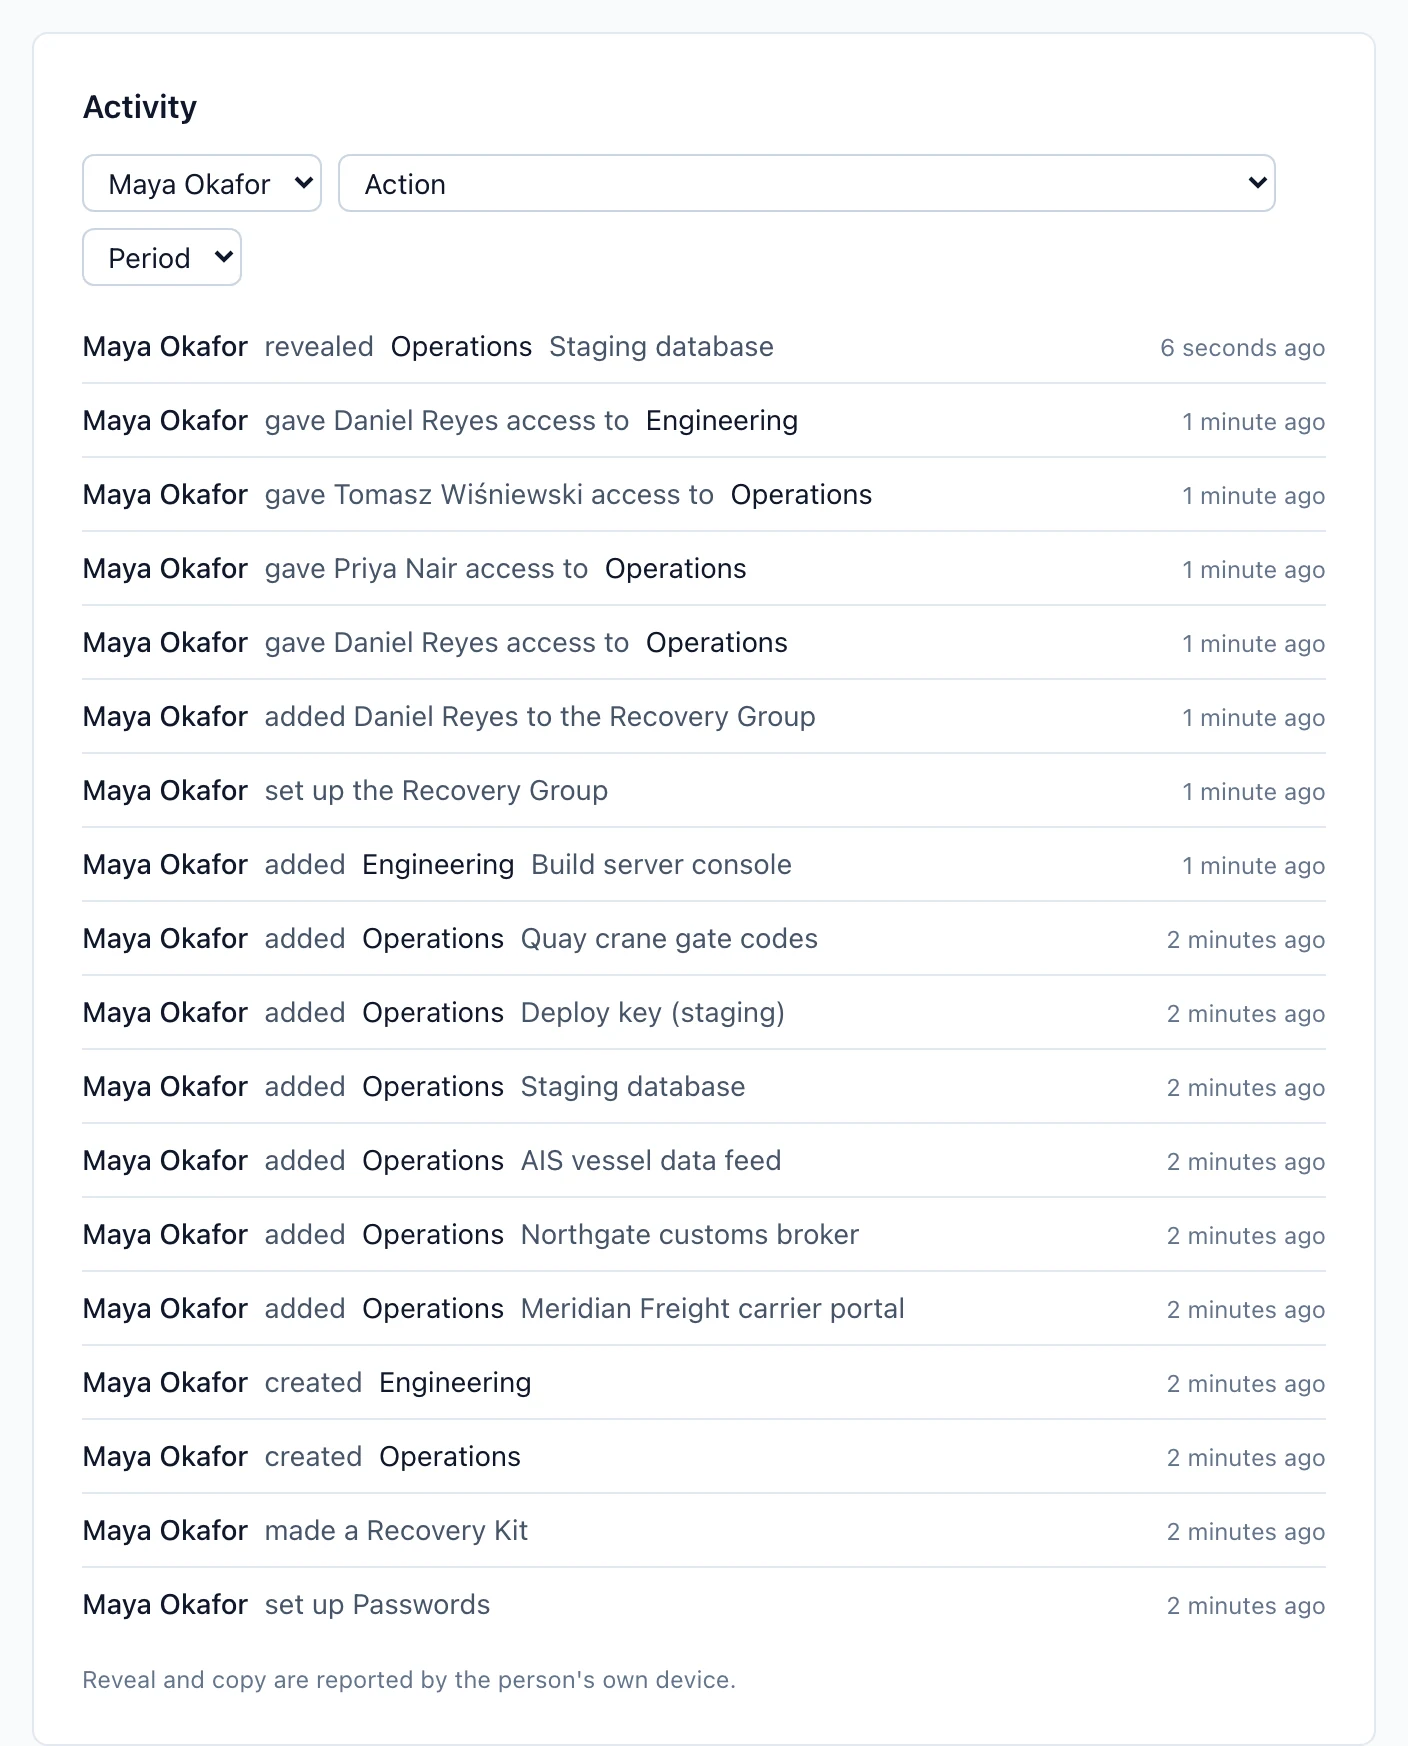
Passwords keeps a log so a workspace can see what happened. Owners and admins see the workspace log under Settings → Passwords → Activity, with filters for vault, person, action and period. People who manage a vault see that vault’s log from its ⋯ menu → Activity.
What is recorded
Items added, changed, moved, deleted and restored; reveals, copies and 2FA code views; imports and exports; people given or removed from a vault; key updates; security events such as devices approved or removed, Recovery Kits made or used, and Recovery Group changes; and agent access: requests, grants, declines, revocations, key releases for Automation vaults, each time a value was applied, a workstation stopped because its output carried a credential, and a manager allowing agents to use a paused item again. Each row has who, what, which vault and when. An item’s title is shown only to people who can open that vault; others see “an item”.
In the workspace log, a Private vault shows security events only, without item names, and counts for the rest.
What is self-reported
Reveal and copy are reported by the person’s own device, which 3mote cannot check. A report that arrives late is marked “reported late”. The table says so under any rows of that kind.
How long it is kept
How long depends on what was recorded.
- Reveals, copies and 2FA code views are kept for your plan’s window: Free 30 days, Team 1 year, Enterprise 7 years.
- Everything else, such as items added, changed, moved or deleted, imports and exports, sharing, devices, keys, recovery and agent access, is kept for at least a year on every plan, and for the plan’s window where that is longer.
Each row’s retention is fixed when it is written, so a later plan change does not shorten or lengthen what is already recorded.